
Developers: 5 Transcription API Security Checks You Can Test
Yes, a transcription API can be integrated securely, but only if the provider gives you five specific controls to verify: TLS 1.2+ in transit, encryption at rest through a key management system (KMS), scoped and short-lived authentication tokens, documented retention windows with auto-delete, and HMAC-signed webhooks. The sections below explain how to test and implement each one, including where OpenTranscription fits the checklist.
TL;DR:
- Ensure the provider uses TLS 1.2 or higher for all REST and WebSocket connections and supports encryption at rest with customer-managed keys for better control.
- Store API credentials securely server-side, issue scoped tokens for streaming, and regularly test token expiry and scope to prevent unauthorized access.
- Validate retention policies with explicit auto-delete timeframes, confirm the existence of delete APIs, and verify redaction capabilities specific to your data privacy needs.
- Prefer private network options like VPC endpoints for sensitive data and implement strict IAM policies with tag-based access controls to limit permission scope.
- Confirm webhook payloads include HMAC signatures for validation, enforce replay protection, and obtain detailed audit logs and compliance attestations from providers.
Table of Contents
- Transcription API Security Checklist for Procurement Review
- Authentication and Token Management Best Practices
- Encryption Expectations: Transport, at Rest, and KMS Controls
- Data Handling: Retention Windows, Deletion, and Redaction
- Network-Level Protections: Private Endpoints and Signed URLs
- Access Control: IAM Roles, Least Privilege, and Tagging
- Key Management: Rotation, CMKs, and Encryption Context
- Monitoring, Webhooks, and Incident Response Expectations
- Compliance and Certifications Worth Requesting
- Developer Implementation Patterns You Can Adopt Today
- How OpenTranscription Supports These Security Controls
- Rate Limiting and Throttling: Preventing API Abuse
- Protecting Against Injection, Replay, and CSRF Attacks
- Secure Integration and SDK Usage Guidelines
- Data Anonymization and Pseudonymization Techniques
- Incident Recovery and Breach Notification Procedures
- Where Privacy, Latency, and Cost Actually Trade Off
- Getting Started With OpenTranscription’s Secure API
- Sources
- FAQ
Transcription API Security Checklist for Procurement Review
Before signing a contract or wiring up an SDK, run every candidate provider through the same set of checks. Treat this as a gate, not a formality. Most vendor security pages read well until you ask for the underlying evidence.
- Transport encryption: Confirm TLS 1.2 or higher on both REST and WebSocket endpoints. You can verify this from the command line with
openssl s_client -connect api.example.com:443 -tls1_2and checking the handshake response. - Encryption at rest: Ask whether stored audio and transcripts use server-side encryption, and specifically whether SSE-KMS or customer-managed keys are available rather than only provider-managed defaults.
- Retention and deletion: Request the exact retention TTL in writing and confirm whether deletion happens automatically or only on request.
- Role-based access: Ask how the provider isolates data between tenants, and whether staff access to raw audio requires a documented approval path.
- Compliance claims: Don’t accept “HIPAA-compliant” or “SOC 2 certified” at face value. Request the actual attestation report and check its scope and date.
- Webhook signing: Confirm webhook payloads carry an HMAC signature you can validate against a shared secret.
- Data locality and subprocessors: Ask for a current subprocessor list and whether audio can be pinned to a specific region.
Red flags include unencrypted storage buckets, transcripts retained indefinitely by default, webhooks with no signature field, and a subprocessor list the vendor won’t provide in writing. Microsoft’s own guidance on speech-to-text services stresses defense-in-depth and transparency about data handling as baseline expectations, not premium add-ons.
Pro Tip: Ask the vendor’s sales engineer to walk through a live decrypt operation in their KMS console. If they can’t show you an audit trail of who decrypted what and when, treat that as a disqualifying gap, not a minor omission.
Authentication and Token Management Best Practices
Authentication mistakes cause more transcription API breaches than any encryption flaw, largely because credentials get pasted into frontend JavaScript where anyone with browser dev tools can read them. Treat every API key, client secret, or full-scope token as a high-risk asset, never as a configuration convenience.
- Keep secrets server-side. Store
client_idandclient_secretin a secret manager (AWS Secrets Manager, HashiCorp Vault, or an equivalent), never in frontend bundles, mobile app binaries, or public repositories. - Issue scoped tokens for streaming. For browser-based real-time transcription, have your backend request a short-lived token limited to a streaming scope, such as
openid transcribe, using an OAuth2 client-credentials grant. Corti’s authentication documentation walks through exactly this backend-to-browser token pattern, and it’s worth modeling your own flow on it. - Rotate on any suspicion of compromise. Build key rotation into your operational runbook rather than treating it as an emergency-only procedure, and assign a separate service account per environment (development, staging, production).
- Test scope and expiry directly. Issue a token, wait past its stated expiry, and confirm the API actually rejects it. Then attempt an out-of-scope call (say, an admin action with a streaming-only token) and confirm it’s refused rather than silently allowed.
Pro Tip: If a provider’s quickstart guide tells you to hardcode an API key into a client-side snippet “for testing,” that pattern tends to survive into production far more often than teams admit. Build the backend proxy from day one.
Encryption Expectations: Transport, at Rest, and KMS Controls
Encryption in transit is table stakes: require TLS 1.2 or higher on both REST and WebSocket connections, and for higher-assurance environments, ask whether the provider supports mTLS or certificate pinning. Amazon’s guidance for building secure applications on Amazon Transcribe specifies TLS 1.2+ for streaming connections as a minimum, alongside support for SSE-KMS and SSE-S3 at rest.
Encryption at rest is where providers diverge more sharply. A provider using only its own managed keys gives you no way to independently revoke access or prove who could decrypt your audio. Server-side encryption with customer-managed keys (CMKs) through a KMS changes that: you control the key lifecycle, you can revoke it unilaterally, and you get an audit trail tied to your own AWS, Google Cloud, or Azure account rather than the vendor’s internal systems.
- Ask whether SSE-KMS or CMK support exists for both audio storage and transcript storage, not just one.
- Request sample KMS audit logs showing decrypt operations and the calling principal.
- IBM’s documentation for its speech-to-text service specifies AES-256 encryption at rest paired with TLS 1.2 in transit, which is a reasonable industry baseline to compare against.
- Never place sensitive values, such as a customer ID or a fragment of PII, inside a KMS encryption context field. That field is used for authenticated metadata, not confidential data, and providers can log it in plaintext.
Data Handling: Retention Windows, Deletion, and Redaction
Retention policy is often the weakest link in an otherwise strong security posture, mostly because it’s easy to overlook during procurement and hard to verify after the fact. Insist on an explicit retention TTL in writing, not a vague “we don’t keep data longer than necessary” statement, and prefer providers that expose deletion as an API call rather than a support ticket.
- Request documented auto-delete behavior with a stated timeframe (24 hours, 30 days, and so on) for both raw audio and generated transcripts.
- Ask whether an API-driven delete endpoint exists, and whether it triggers account-wide erasure or only a single job’s data.
- Understand the redaction trade-off: some providers support automated PII redaction on batch jobs but only real-time PII identification, without redaction, on streaming jobs. Amazon Transcribe documents this exact split between batch and streaming redaction support, which matters if you’re processing call center audio with credit card numbers spoken aloud.
- Decide whether server-side redaction is sufficient or whether you need client-side pre-redaction, stripping identifiable content before it ever leaves your infrastructure.
To validate any of this, submit a test job containing obviously fake but structured PII (a dummy phone number or account ID), request deletion through the provider’s documented mechanism, then confirm removal on the stated timeline rather than trusting the dashboard’s “deleted” label.
Network-Level Protections: Private Endpoints and Signed URLs
Regulated workloads, healthcare audio under HIPAA, financial call recordings, or high-value enterprise customer data, generally justify private connectivity options like VPC endpoints, AWS PrivateLink, or Direct Connect, which keep traffic off the public internet entirely. Amazon’s Transcribe security guidance treats private connectivity as the recommended pattern for sensitive workloads, while acknowledging it costs more and adds operational complexity than standard TLS over the public internet.
Be cautious with signed URLs for audio upload or transcript retrieval. A signed URL grants access to anyone holding the link for its valid window, with no additional authentication check. For sensitive audio, an authenticated POST request using a short-lived, scoped token is a tighter pattern than a bearer-style signed URL that could leak through a browser history or a forwarded email.
Access Control: IAM Roles, Least Privilege, and Tagging
Distributing long-term credentials to individual developers or services is one of the more common ways transcription pipelines get compromised. Issue short-lived roles per service instead, and keep separate service accounts for development, staging, and production so a leaked staging credential can’t touch production audio.
- Apply tag-based or attribute-based access controls to transcription jobs and storage buckets, so a policy can restrict access by project, environment, or data classification rather than granting blanket bucket-level permissions.
- Review IAM policies for over-broad wildcard permissions (
s3:*instead ofs3:GetObjectscoped to a specific prefix, for instance) on any bucket holding audio or transcripts. - Confirm the provider maintains access review logs for the KMS keys and storage resources tied to your account, and that you can request them during an audit.
Key Management: Rotation, CMKs, and Encryption Context
Customer-managed or tenant-managed keys give you control a provider-managed default key never will: you decide the rotation cadence, and you can revoke access immediately if a key is suspected compromised, without waiting on a vendor support ticket. Document that rotation schedule and your emergency revocation procedure before you need them, not during an incident.
Keep encryption context fields limited to non-sensitive metadata, a job ID or environment tag, never a customer name, account number, or anything personally identifying. AWS’s guidance on Transcribe security specifically recommends reviewing KMS audit logs for decrypt operations and the calling principal as proof that access controls are actually enforced, not just configured. Ask providers for that same evidence directly. A vendor that can’t produce it likely isn’t logging decrypt operations at the granularity you’d need for an audit.
Monitoring, Webhooks, and Incident Response Expectations
Access and audit logs for every transcript read and KMS decrypt operation are non-negotiable for any workload handling sensitive audio. Ask how long the provider retains those logs and what format you’ll receive them in during an audit.
- Confirm webhook deliveries carry an HMAC-SHA256 signature you can validate against a shared secret, a pattern Capvo documents clearly in its published security controls, including hashed API key storage and immediate revocation on compromise.
- Test webhook replay protection by resending a captured payload and confirming the endpoint rejects it rather than reprocessing the job.
- Ask directly about breach notification timelines: how quickly you’d be told, and through what channel, if the provider suffered an incident touching your data.
Pro Tip: Build your own webhook signature verification into a unit test that runs in CI. It’s a five-minute implementation that catches a provider silently changing their signing algorithm before it breaks production.
Compliance and Certifications Worth Requesting
ISO 27001 and SOC 2 function as baseline security attestations for most B2B transcription providers, covering general information security management and operational controls, respectively. For healthcare audio specifically, HIPAA eligibility, sometimes paired with SOC or HITRUST reporting, becomes relevant, and you should ask for a scoped audit report rather than accepting a marketing badge.
Beyond certifications, require a signed Data Processing Agreement (DPA) and a current subprocessor list before integration, particularly if you operate under GDPR or a similar regional data protection regime. If data locality matters for your compliance posture, get explicit commitments on where audio and transcripts are stored and processed, in writing, not implied by a vendor’s headquarters location. When validating any certification claim, request the actual attestation document and confirm its scope covers the specific service you’re integrating, not just the vendor’s broader corporate entity.
Developer Implementation Patterns You Can Adopt Today
These patterns require no special negotiation with a vendor. You can build them into your integration regardless of which transcription API you choose.
- Streaming auth flow: authenticate the user in your app, have your backend request a limited-scope, short-lived token from the provider, open the WebSocket connection using that token, and refresh it before expiry to avoid a dropped session mid-stream.
- REST proxy pattern: route all REST calls through your backend rather than calling the provider directly from a client. Your backend injects the real credential, validates the payload, and enforces per-user quotas and authorization.
- Webhook verification: on receipt, compute the HMAC-SHA256 signature using your shared secret and compare it to the header value; check the timestamp or nonce to reject replayed deliveries.
- Pre-redaction for sensitive audio: when policy requires minimizing data shared with any third party, run a lightweight local PII filter before upload rather than relying solely on provider-side redaction.
Pro Tip: Corti’s documentation includes a concrete example of the client-credentials token request format for streaming scopes. Use it as a template even if you’re integrating with a different provider; the pattern generalizes well.
How OpenTranscription Supports These Security Controls
OpenTranscription’s API is built around the same checklist outlined above: real-time streaming over TLS, per-second billing with no opaque subscription terms, and a benchmarking layer across 40+ models so you can weigh security posture, latency, and cost side by side, instead of guessing. With support for 105+ languages and speaker diarization built into the model catalog, developers can select a model that matches both accuracy needs and data handling requirements for a given workload. The platform overview documents retention settings and integration options for teams evaluating providers against the controls covered in this article.
Rate Limiting and Throttling: Preventing API Abuse
Rate limits exist to protect both the provider’s infrastructure and your own account from abuse, whether that’s a runaway retry loop in your own code or a leaked key being hammered by someone else. Most transcription APIs enforce limits at multiple levels: requests per second, concurrent streaming connections, and total audio minutes processed within a billing window.
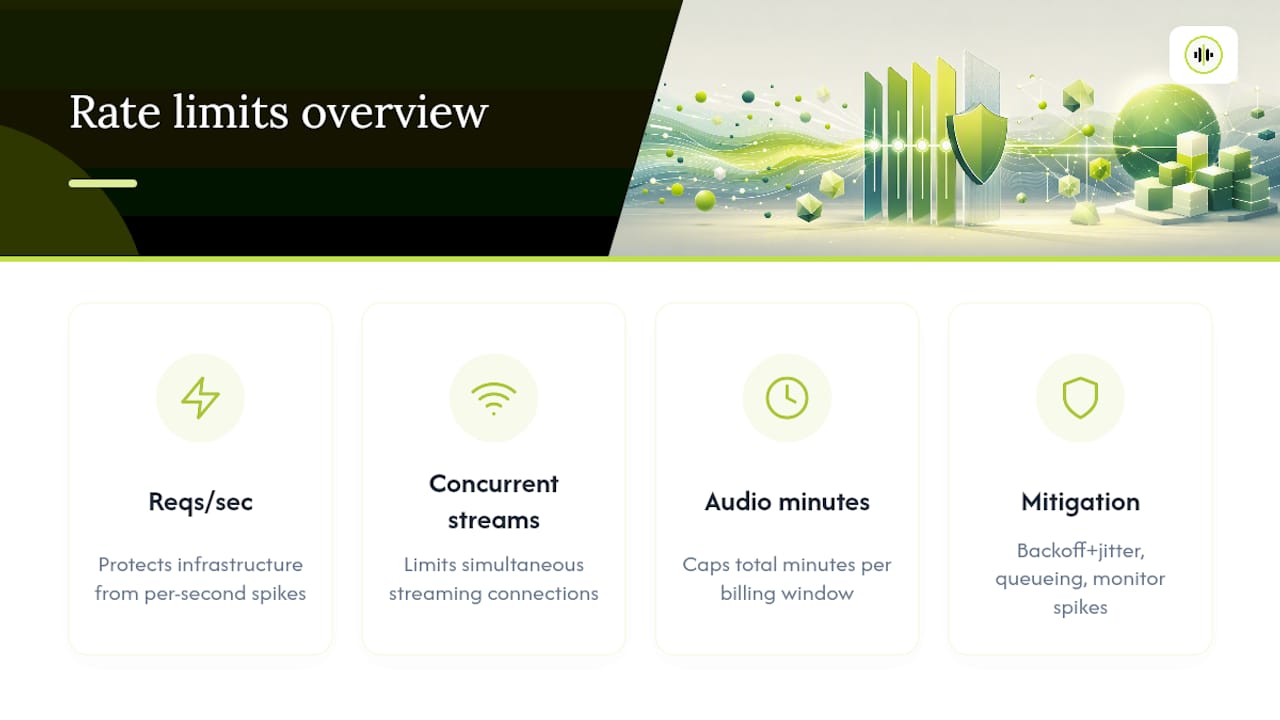
Design your integration to respect documented limits from the start rather than discovering them through 429 responses in production. Implement exponential backoff with jitter when you receive a rate-limit response, and cache or queue requests locally during traffic spikes instead of firing them all simultaneously. If your application handles bursty traffic (a podcast platform processing a batch upload after a new episode drops, for instance), ask the provider whether burst allowances or queue-based processing options exist rather than a hard per-second ceiling.
Throttling also serves as an early warning system for credential compromise. A sudden spike in requests from a token that normally handles modest, predictable traffic is a signal worth alerting on, not just absorbing. Pair your own application-level monitoring with the provider’s rate-limit headers (commonly X-RateLimit-Remaining or similar) so you can react before hitting a hard cutoff. Providers that expose granular, documented rate limits per endpoint, rather than a single undocumented global ceiling, make this kind of proactive monitoring meaningfully easier to build.
Protecting Against Injection, Replay, and CSRF Attacks
Transcription APIs face the same attack surface as any REST or WebSocket service, plus a few wrinkles specific to audio processing. Injection risks typically show up in metadata fields (custom vocabulary lists, speaker labels, or callback URLs) rather than the audio payload itself, since audio is binary data the API doesn’t parse as executable input. Sanitize and validate every metadata field your backend passes through to the provider, treating it with the same scrutiny you’d apply to a SQL query parameter.
Replay attacks matter most at the webhook layer, where a captured payload could be resent to trigger duplicate processing or spoof a completed job. Validating an HMAC signature alone isn’t sufficient protection. Pair it with a timestamp or nonce check, rejecting any delivery older than a defined window (five minutes is a common default) even if the signature itself is valid.
CSRF is less relevant to server-to-server API calls but becomes a real concern the moment you expose any transcription-triggering action through a browser-based form or dashboard. Standard mitigations apply: use anti-CSRF tokens on state-changing requests, verify the Origin or Referer header on sensitive actions, and never allow a GET request to trigger a transcription job or deletion, since GET requests are far easier to trigger unintentionally through a crafted link. Treat every provider-issued webhook endpoint you build as a public-facing attack surface, because it is one.
Secure Integration and SDK Usage Guidelines
Official SDKs save development time, but they also inherit whatever security posture the provider baked in, so review them with the same scrutiny you’d apply to the raw API. Pin SDK versions in your dependency manifest rather than tracking latest, and subscribe to the provider’s release notes or security advisories so a patched vulnerability doesn’t sit unaddressed in your production build for months.
Audit what an SDK actually logs by default. Some libraries log full request and response payloads for debugging, which can mean audio metadata or transcript snippets ending up in your application logs, plaintext, outside any encryption boundary the provider maintains. Disable verbose logging in production or scrub sensitive fields before they hit your log pipeline.
Avoid granting an SDK broader filesystem or network permissions than it needs. A transcription SDK that requests unrestricted outbound network access, beyond the provider’s documented endpoints, is worth a closer look at its dependency tree. Where the provider offers a lightweight HTTP client alongside a heavier full-featured SDK, the lighter option often gives you more visibility into exactly what’s being sent and reduces your supply-chain exposure to a smaller set of dependencies. Finally, run SDK dependencies through a vulnerability scanner (Dependabot, Snyk, or an equivalent) as part of your normal CI pipeline, not as a one-time check during initial integration.
Data Anonymization and Pseudonymization Techniques
Anonymization and pseudonymization solve different problems, and conflating them leads to compliance gaps. Anonymization strips identifying information irreversibly, meaning no key or process can reconstruct the original identity. Pseudonymization replaces identifiers with a token or reference that can be reversed given the right key, useful when you need to reassociate a transcript with a customer record later for legitimate business reasons.
For transcription workflows, pseudonymization usually looks like replacing a caller’s name or account number with a stable token before the audio or transcript reaches the provider, storing the mapping table separately, under stricter access control, in your own systems. This limits what a provider breach could expose, since the transcript alone wouldn’t reveal the underlying identity.
True anonymization is harder to achieve with speech data than with structured records, because voice itself is a biometric identifier. Removing a name from a transcript doesn’t anonymize the underlying audio if the voice remains attached and could be matched against another recording. If your compliance obligations require genuine anonymization rather than pseudonymization, that likely means discarding the raw audio entirely once a transcript is generated and validated, keeping only the redacted text. Decide which standard your workload actually requires before building the pipeline, since retrofitting anonymization after audio has already been stored is far harder than designing for it upfront.
Incident Recovery and Breach Notification Procedures
Ask every transcription provider, before signing anything, what their documented breach notification timeline looks like and through what channel you’d be informed. A vague “we’ll let you know if something happens” is not a policy; a stated commitment (notification within a specific number of hours or days of confirmed impact) is something you can hold a vendor to contractually.
Build your own incident response runbook assuming the provider notification could be your only warning. That means knowing in advance which of your systems consume transcription data, so you can quickly assess exposure the moment a provider discloses an incident. Maintain a current inventory of which API keys, service accounts, and webhook endpoints are tied to which provider, so revocation during an incident is a five-minute task rather than a scramble through old documentation.
Test your own recovery path periodically: rotate a key, confirm the old one stops working immediately, and confirm your application handles the rotation gracefully rather than throwing unhandled errors. If a provider breach does occur, your speed advantage comes almost entirely from preparation done beforehand, not from any capability the provider itself offers during the incident.
Where Privacy, Latency, and Cost Actually Trade Off
Private endpoints and customer-managed keys make sense for healthcare audio, financial recordings, or any workload with a named regulatory obligation. For everything else, scoped tokens with tight expiry and a short retention window usually deliver equivalent real-world protection at a fraction of the operational cost.
Start with secure defaults (TLS, scoped tokens, short retention) and harden selectively as compliance requirements actually demand it, rather than over-engineering from day one. Test your assumptions early: expire a token deliberately, replay a webhook, and request a deletion. If those three tests pass, your foundation is probably sound.
— Benjamin
Getting Started With OpenTranscription’s Secure API
OpenTranscription is built for developers who need the checklist covered in this article without negotiating each control individually. Real-time streaming runs over encrypted connections, retention settings are configurable rather than fixed at “forever” by default, and transparent per-second billing means you’re never locked into a subscription tier just to access stronger data controls.
Because the platform benchmarks 40+ transcription models side by side, you can weigh accuracy and latency against your specific security requirements instead of guessing which model handles sensitive audio best. The model rankings page lets you compare providers on cost and performance before you commit to an integration, and the realtime rankings narrow that comparison specifically for streaming workloads where token expiry and connection security matter most. For a deeper look at implementing encrypted API calls and access control in your own stack, Paid Lens’s security documentation covers complementary patterns for HTTPS enforcement and access control worth reviewing alongside your integration. Start by reviewing the platform overview and pulling API credentials into a sandbox environment to test scoped tokens and webhook signatures before your first production job.
Sources
- Best practices for building secure applications with Amazon Transcribe | Artificial Intelligence
- Security Best Practices — Corti docs
- Data, privacy, and security for Speech to text - Foundry Tools
- Security · Capvo
FAQ
What Is the Best Transcription API for Security?
The strongest choice is whichever provider gives you verifiable, documented controls, TLS 1.2+, KMS-backed encryption at rest, scoped tokens, and signed webhooks, rather than one that simply markets itself as “secure.” OpenTranscription exposes these settings alongside transparent pricing, letting you compare model options without a subscription commitment.
What Does API Security Mean for Transcription Services?
API security for transcription means protecting audio and transcript data at every stage: encrypted transport, encrypted storage, authenticated and scoped access, controlled retention, and verifiable webhook integrity. It covers both the data itself and the credentials used to access it.
How Do I Check if a Transcription API Is Safe?
Request the provider’s TLS configuration, ask for KMS or encryption-at-rest documentation, test token expiry and scope directly, and confirm webhook payloads carry an HMAC-SHA256 signature you can validate. If a vendor can’t produce audit logs showing decrypt operations, treat that as a gap.
What Are the Main Risks of Using Transcription APIs?
The most common risks are exposed credentials in frontend code, unclear or indefinite data retention, unsigned webhooks vulnerable to replay, and vague compliance claims that don’t hold up when you request the underlying attestation report. Each has a concrete, testable fix covered in this guide.